AI Security & Governance

Use AI without exposing your customers' data

AI Security & Governance

Protect Your Customer Data While You Use AI

Your team is already using AI: chatbots on the website, assistants reading the inbox, tools that summarize customer calls, automations that move data between systems. Each one is a new place customer information can leak, and a new way for an outsider to make your systems do something you never intended.

We help small and mid-sized businesses find those risks, test them the way an attacker would, fix them, and keep watching, with findings grounded in published frameworks that stand up in front of a board, an auditor, or an insurer.

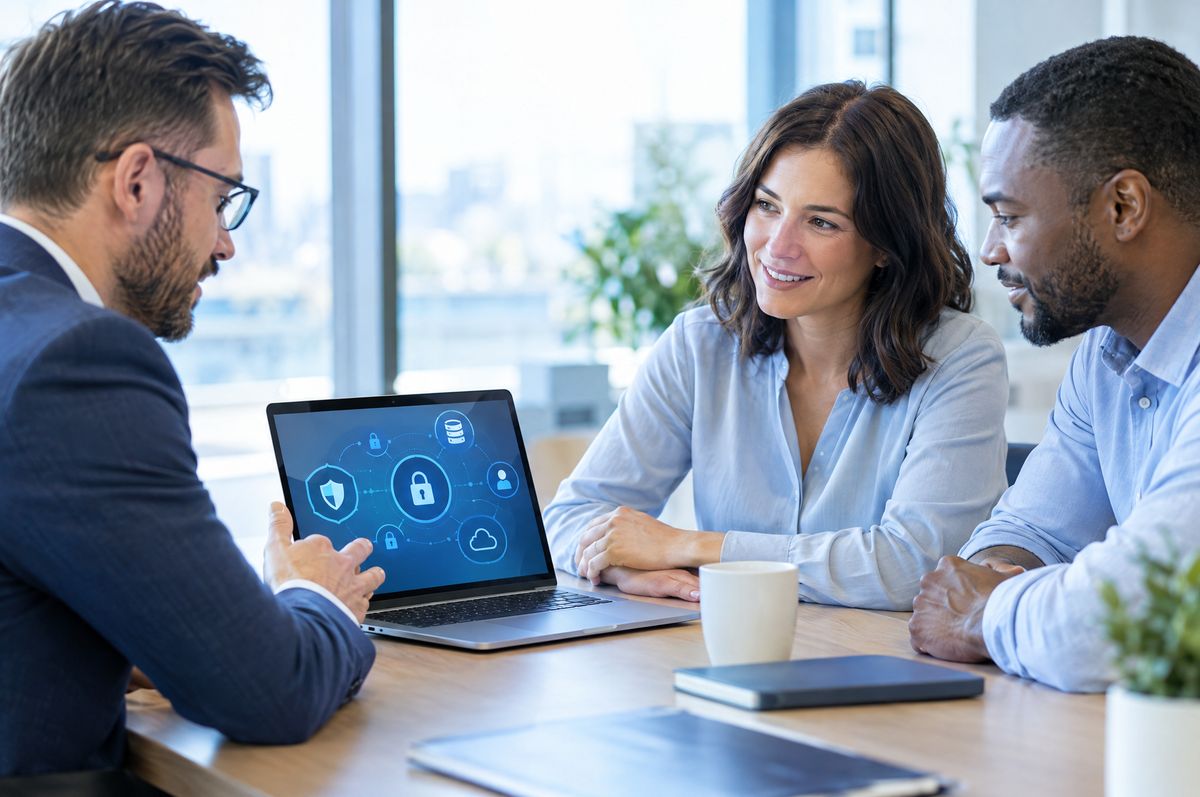
A consultant reviewing a data privacy diagram with a business owner
Assess. Test. Fix. Monitor.

A clear path from not knowing where your AI risks are to having them found, fixed and watched.

Our Services

Five Ways We Keep Your AI Safe

Find every AI tool in use, map where customer data flows, and get a prioritized list of what to fix. The usual starting point.

We attack your chatbots, assistants and agents, with your written permission, to find prompt injection and data leaks before someone else does.

Ongoing tests that catch when an AI system's answers get worse, riskier, or start revealing things they shouldn't.

Policies, an AI inventory, approval rules and staff training, so AI use is decided rather than discovered.

New AI automations built with least-privilege access, personal data masked before it reaches a model, logging, and retention limits from day one.

Our own site and client portal follow the same rules. See How We Protect Your Data and our AI Use Policy.

Industries We Serve

Built for Businesses That Answer for Their Data

Use AI with the controls your examiners expect.

Save time with AI without putting patient information at risk.

Use AI on client work without risking taxpayer data or your license.

Adopt AI in a way you can explain at a public meeting.

Frameworks we map to

  • NIST AI Risk Management Framework (AI RMF 1.0) for overall AI risk and governance.
  • OWASP Top 10 for LLM Applications for the vulnerabilities we test chatbots and assistants against.
  • MITRE ATLAS for describing how attacks on AI systems actually work.
  • ISO/IEC 42001 for clients working toward an AI management system standard.
We practice what we recommend. How We Protect Your Data describes the safeguards on this site and our client portal, and our AI Use Policy sets the rules for how we use AI with your data.
Get Started

Start With a Scoping Call

Thirty minutes, by video or on-site. We will talk through how your business uses AI today and where customer data goes, and you will leave with a written scope and quote. Nothing is tested and no data is shared until a written agreement is signed.

Schedule a Scoping Call Send a Question

I am Larry Collett, the AI Expert and Automation Workflow developer in Charleston, SC and the surrounding Lowcountry area.